About

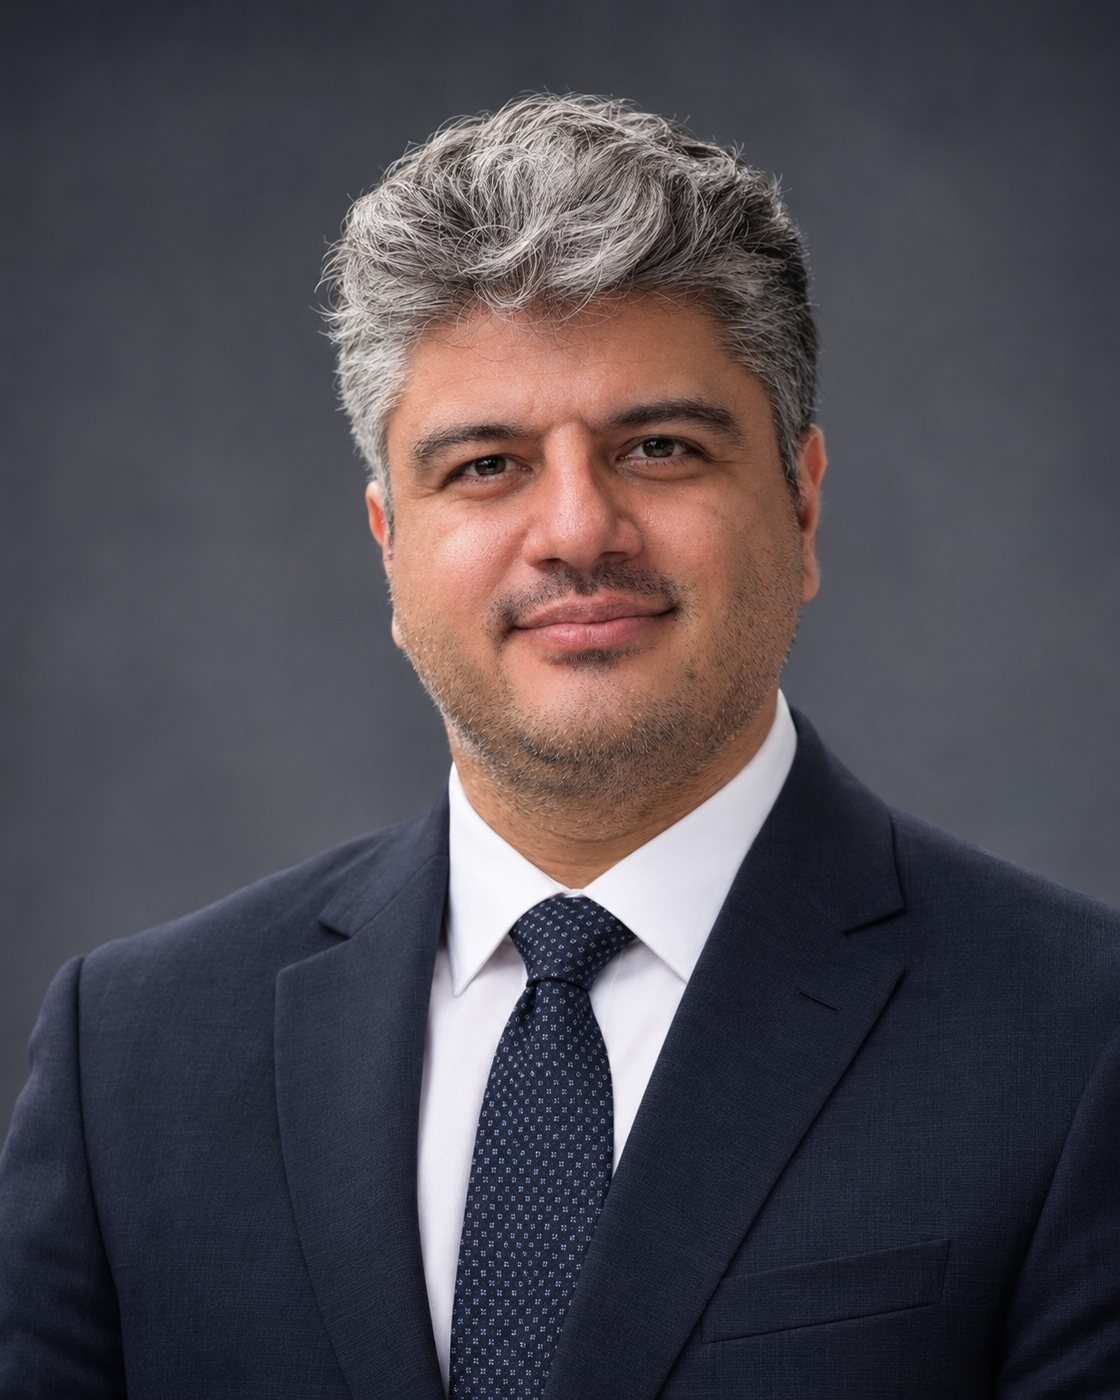
Sina Manavi

Information security and cybersecurity executive, strategic adviser and published author.

Sina Manavi, information security and cybersecurity executive

Who I am

Biography

Sina Manavi is an information security and cybersecurity executive with more than 19 years of experience across global logistics, insurance, banking and security consulting. As Global Head of Cloud & AI Security, Compliance & Resiliency at DHL IT Services, he leads security architecture, compliance, identity and access management and security operations for cloud platforms worldwide, and serves as the organisation's AI Security Champion.

His career began in application security and penetration testing, moved through consulting and postgraduate research, and continued into regional security leadership at CIMB Group and AIA Group, where the work shifted from finding weaknesses to governing risk across Asia-Pacific.

He is the co-author of Securing Cloud Containers (Wiley, 2025), a technical reviewer for Wiley and Packt, and a contributor to CIO and CSO Online. He holds an MSc in Computer Science (Security) and the CCISO, CISM, CISA, CDPSE and ISO/IEC 27001 Lead Auditor credentials.

Currently Global Head of Cloud & AI Security, Compliance & Resiliency DHL IT Services

Written and maintained by Sina Manavi. Independent sources for publications, appearances and recognition are listed on the Bio & Media page, which also has the full biography for event organisers.

Career

From application security to global leadership

Three chapters, most recent first: security leadership at global scale, built on governance in regulated industries and, before that, technical depth.

Global leadership · 2022 – today

Security at global scale

Leading cloud and AI security, compliance and resiliency for a global enterprise across four cloud providers: building teams across architecture, engineering, identity, compliance and operations, achieving global ISO/IEC 27001 certification for public cloud and, as AI Security Champion since 2024, setting the standards for adopting generative and agentic AI safely. In parallel came a Wiley book, editorial writing and industry recognition.

  • Global Head of Cloud & AI Security, Compliance & ResiliencyDHL IT ServicesFeb 2022 – Present

Regional leadership · 2016 – 2022

From controls to governance

In regulated banking and insurance across Asia-Pacific, the work moved from finding weaknesses to governing risk. At CIMB Group: security architecture standards, threat intelligence and the regional security operations centre. At AIA Group: regional cyber security governance and risk management, ISO/IEC 27001 certification across entities, and executive dashboards that put cyber risk in front of leadership.

  • Senior Manager, Group Information Security (Regional, Asia-Pacific)AIA GroupFeb 2020 – Feb 2022
  • Senior Manager, Regional IT SecurityCIMB GroupJun 2016 – Dec 2019

Foundations · 2007 – 2016

The practitioner years

A career that began hands-on: designing application security architecture, reviewing code and testing web, mobile and network defences. Consulting followed, in penetration testing, digital forensics and security posture assessment, alongside postgraduate research on cloud virtualisation security published through IEEE. These years built the technical judgement that later leadership depends on.

  • Information Security ConsultantKaapagam TechnologiesApr 2015 – Jun 2016
  • Information Security ConsultantCondition ZebraJan 2014 – Dec 2014
  • Application Security ConsultantIRSA ShabakehSep 2007 – Dec 2010

Milestones

The journey, year by year

  1. Foundations ·

    Application security

    Begins a security career as an application security consultant: designing an application security architecture framework, leading source code review and testing web, mobile and network security.

    Read more: Application security (2007)
  2. Research ·

    Cloud security research

    Postgraduate research at Universiti Putra Malaysia on securing cloud virtualisation; lead author of the Hierarchical Secure Virtualization Model, published at IEEE CyberSec 2012.

    Read more: Cloud security research (2012)
  3. Consulting & speaking ·

    Security consulting and the first stages

    Penetration testing, digital forensics and security advisory for clients; co-authors IEEE research on cloud identity management and begins speaking at industry events in Malaysia.

    Read more: Security consulting and the first stages (2014)
  4. Banking ·

    Regional IT security leadership at CIMB

    Leads regional cybersecurity across Asia-Pacific for CIMB Group: security architecture, threat intelligence and the regional security operations centre.

    Read more: Regional IT security leadership at CIMB (2016)
  5. Insurance ·

    Group information security at AIA

    Leads regional cyber security governance and risk management across Asia-Pacific for AIA Group, including ISO/IEC 27001 certification across regional entities.

    Read more: Group information security at AIA (2020)
  6. Global leadership ·

    Global head of cloud and AI security

    Joins DHL IT Services to lead cloud security, compliance and resiliency globally across Azure, Google Cloud, AWS and OCI, building teams across architecture, engineering, IAM, compliance and security operations.

    Read more: Global head of cloud and AI security (2022)
  7. AI security ·

    AI Security Champion

    Appointed AI Security Champion: defining enterprise AI security and governance standards, leading AI risk assessments and overseeing ISO/IEC 42001 readiness.

    Read more: AI Security Champion (2024)
  8. Author ·

    Securing Cloud Containers, published by Wiley

    Co-authors a 352-page practitioner guide to cloud-native security, and introduces the MAESTRO framework for generative and agentic AI to CSO Online readers.

    Read more: Securing Cloud Containers, published by Wiley (2025)
  9. Recognition ·

    Cloud Security Leader of the Year

    Recognised as Cloud Security Leader of the Year at the DCCI Awards 2026 in Malaysia; panellist at CyberSecMalaysia 2026 on identity as enterprise infrastructure; writes for CIO on how AI is changing technical hiring.

    Read more: Cloud Security Leader of the Year (2026)

Expertise

Seven connected domains

Information security leadership means enabling an organisation to pursue its strategy, adopt new technology and keep the trust of customers, regulators and partners, while holding risk within appetite and accountability clear at every level.

How this expertise informs strategic advisory

Qualifications

Education & credentials

Education

  • MScMaster of Science in Computer Science (Security) · Universiti Putra Malaysia · 2015
    Research on cloud virtualisation security, identity management and digital forensics. Thesis: Digital Forensics Investigation Framework for Raspberry Pi (2015).
  • BEngBachelor of Engineering in Software Engineering · Islamic Azad University, Lahijan · 2010

Professional certifications

  • CCISOCertified Chief Information Security Officer · EC-Council · since 2021
  • CISMCertified Information Security Manager · ISACA · since 2021
  • CISACertified Information Systems Auditor · ISACA
  • CDPSECertified Data Privacy Solutions Engineer · ISACA · since 2020
  • ISO 27001 LAISO/IEC 27001:2013 Lead Auditor · GAQM · since 2021
  • CHFIComputer Hacking Forensic Investigator · EC-Council · since 2014
  • CEHCertified Ethical Hacker · EC-Council · held 2013–2016

Selected training

  • Microsoft Copilot for Security Ninja TrainingMicrosoft
  • Foundations of Purple TeamingAttackIQ
  • CISSP preparation courseCybrary
  • COBIT Foundation
  • Advanced Web Hacking & DefenceINFORISK360

Professional memberships

  • ISACAProfessional member, ISACA · 2016 – present
  • AISAProfessional member, Australian Information Security Association · March 2021 – present
Professional community

Community & collaboration

  • Speaker and contributor, OWASP Foundation

    Talks and community contributions on application and mobile security.

    Self-described
  • Volunteer adviser, Mendeley

    Volunteer adviser for the Mendeley research-collaboration platform during academic research years.

    Self-described

Perspective

Values & professional philosophy

  • Security as a business enabler

    Security earns its place by helping the organisation move faster, with confidence.

  • Evidence over assertion

    Controls should produce evidence continuously. Assurance that depends on an annual effort is assurance in name only.

  • Design for disruption

    Resilient organisations assume that disruption will happen and engineer their recovery before they need it.

  • Accountability travels with autonomy

    As AI systems begin to act on behalf of the enterprise, every action needs an accountable owner, a governed identity and an audit trail.

Looking ahead

  • Board-level governance of cyber and technology risk
  • Security and governance of agentic AI
  • Research collaboration between industry and academia
  • Developing the next generation of security leaders
  • Secure innovation in start-ups and growing companies
  • Resilience of critical services and global supply chains

Explore further

Ideas behind the story

Published work, and the executive perspectives this career informs.